

Fintech compliance for a payment or crypto firm in the EU or UK comes down to four duties you cannot hand to anyone else. They are the licence, anti-money laundering controls, ICT resilience and the protection of client money. Most of them get a new rulebook, a new supervisor or a hard deadline between now and 2028.
The order matters. The licence decides which rules apply, the AML programme decides whether you keep the licence, and DORA decides how you report the day your systems fail. This guide maps those duties by firm type, lists the dates, and separates the work you can buy from the accountability you cannot.
Key moments
In short
- Your licence sets your rulebook: a payment institution needs EUR 20,000 to 125,000 of initial capital, an e-money institution EUR 350,000, a crypto-asset service provider EUR 50,000 to 150,000.
- The MiCA transition ended on 1 July 2026. Any firm serving EU clients with crypto services without a MiCA licence is now in breach of EU law.
- The EU AML Regulation applies from 10 July 2027, and the new EU AML Authority starts direct supervision of 40 firms in 2028.
- Under DORA, a major ICT incident must be reported within 4 hours of classifying it and no later than 24 hours after you become aware of it. Outsourcing never moves that duty.
What does fintech compliance cover for a payment firm?#
Fintech regulatory compliance is the set of rules a regulated firm must meet to get authorised and to keep the authorisation. For an EU or UK payment or crypto business that means four blocks: authorisation and capital, AML and sanctions, ICT and operational resilience, and conduct rules such as safeguarding client funds. The licence comes first because it decides which version of the other three applies to you.
Capital is the first hard number in that decision. The Payment Services Directive (PSD2, Art. 7) sets initial capital for payment institutions at EUR 20,000, EUR 50,000 or EUR 125,000 depending on the services. The E-Money Directive (Art. 4) requires EUR 350,000 for an e-money institution. MiCA, the EU's crypto-asset regulation, requires a crypto-asset service provider (CASP) to hold the higher of a fixed minimum from Annex IV or one quarter of the previous year's fixed overheads (Art. 67).
| Firm type | EU licence | Minimum initial capital | Who supervises |
|---|---|---|---|
| Payment institution | PSD2 authorisation | EUR 20,000 / 50,000 / 125,000 by service | National authority (UK: FCA) |
| E-money institution | EMD2 authorisation | EUR 350,000 | National authority (UK: FCA) |
| CASP, class 1 (transfers, orders, advice) | MiCA authorisation | EUR 50,000 or 1/4 of fixed overheads | National authority, ESMA register |
| CASP, class 2 (custody, exchange) | MiCA authorisation | EUR 125,000 or 1/4 of fixed overheads | National authority, ESMA register |
| CASP, class 3 (trading platform) | MiCA authorisation | EUR 150,000 or 1/4 of fixed overheads | National authority, ESMA register |
Capital is the smallest part of the cost. The bigger part is people. You need a management body that the supervisor accepts, a compliance officer and a money laundering reporting officer, and enough staff in the licensed entity to run the controls.
Which licence does a fintech need in the EU and UK?#
You need a licence for the activity, not for the technology. Moving money for clients means a payment institution or e-money licence. Exchanging, holding or transferring crypto-assets for clients means a MiCA CASP authorisation in the EU and FCA registration in the UK. If you do both, you need both, and the approval odds are lower than most founders expect.
EU: the MiCA cut-off has passed#
The grace period for crypto firms is over. ESMA's statement on the end of MiCA transitional periods of 17 April 2026 says:
"After this date, any entity providing crypto-asset services to EU clients without a MiCA licence will be in breach of EU law and must cease offering such services."
The date was 1 July 2026. ESMA publishes no headline total, but its interim register file listed about 380 active firms, authorised or notified, as of 22 October 2026, with Germany, France and the Netherlands holding the most. The same statement warns clients that MiCA protection applies only to the authorised legal entity in the EU, not to other companies in its group. What a full file involves is covered in our guide to MiCA CASP licence requirements, and the budget in our breakdown of CASP licence cost.
For payment and e-money firms, PSD2 and the E-Money Directive still apply. Their replacement is close: the payment services package is covered below.
UK: approval rates are low#
The FCA publishes its own outcomes. Its table of approved applications shows about 20% for payment institutions and 40-45% for e-money institutions in 2025, up from 15% and 15-20% in 2024. The FCA aims to decide complete payments and e-money applications within 3 months and incomplete ones within 10 months, a target it set in July 2025.
Crypto firms face a separate gate. They must register with the FCA under the Money Laundering Regulations before they start, even if they already hold an EMI or PI licence. Since January 2020 the FCA has decided 393 crypto registrations and approved 68 of them, or 17%. A further 265 applications were withdrawn, many of them, according to the FCA, once it became clear the firm did not meet the standard.
What AML rules apply to fintechs from 2027?#
Anti-money laundering is where most fintech compliance failures happen and where the EU rulebook changes most. From 10 July 2027 the EU AML Regulation (AMLR, Regulation (EU) 2024/1624) applies directly in every member state, replacing much of the national detail that firms have dealt with until now. The Sixth AML Directive must be transposed by the same date.
A central supervisor arrives with it. According to the EU Anti-Money Laundering Authority, based in Frankfurt, it will select 40 obliged entities for direct supervision during 2027 and start supervising them during 2028. Everyone else stays with the national supervisor, but under rules written and checked at EU level.
Crypto firms are already under a stricter regime. The Transfer of Funds Regulation (EU) 2023/1113, the EU travel rule, has applied since 30 December 2024. According to the European Parliament's summary of the agreed text, originator and beneficiary information must travel with crypto-asset transfers regardless of the amount. EBA guidelines in force from the same date tell CASPs what to do when that information is missing.
Supervisors are not waiting for 2027 to enforce. Three recent cases show the pattern.
- The Central Bank of Ireland fined Coinbase Europe EUR 21,464,734 in November 2025 after 30,442,437 transactions were not fully monitored between April 2021 and March 2025.
- The FCA fined Monzo GBP 21,091,300 in July 2025 for weak financial crime controls during a period of fast growth.
- The Bank of Lithuania fined Revolut Bank EUR 3.5 million in April 2025 for failures in monitoring business relationships and transactions.
Colm Kincaid, Deputy Governor at the Central Bank of Ireland, put the risk this way: "The failure of such a system within any financial institution creates an opportunity for criminals to evade detection – and criminals will take that opportunity."
The common thread is monitoring that did not keep up with growth and volume.
What does DORA require from payment and crypto firms?#
DORA, the Digital Operational Resilience Act (Regulation (EU) 2022/2554), has applied since 17 January 2025. It covers payment institutions, e-money institutions and CASPs, and it turns an ICT outage into a regulatory event with deadlines measured in hours.
The reporting clock under the technical standards has three steps. The initial notification is due within 4 hours of classifying an incident as major, and no later than 24 hours after you become aware of it. The intermediate report follows within 72 hours. The final report is due within one month. According to the European Supervisory Authorities, financial entities reported 3,383 major ICT incidents in 2025, and 16% came from payment firms.
DORA also requires a register of information on every contract for ICT services (Art. 28(3)). In November 2025 the supervisors designated 19 critical ICT third-party providers, including Amazon Web Services, Google Cloud and Microsoft, for direct EU oversight. That oversight sits on top of your duties, not in place of them: you still report the incident, keep the register and test your exit plan if your cloud provider fails.
How do safeguarding and payment rules change by 2027?#
Client-money rules and payment-execution rules both tighten on fixed dates over the next year, while the PSD2 replacement still has no application date. If you hold client funds or send euro payments, three changes need work now.
In the UK, the FCA's new safeguarding regime (PS25/12) came into force on 7 May 2026. Payment and e-money firms must calculate their safeguarding requirement every day, keep a resolution pack and file a monthly return. An annual safeguarding audit is required unless the firm safeguarded no more than GBP 100,000 at any point in the previous 53 weeks.
In the EU, the Instant Payments Regulation (EU) 2024/886 reaches payment and e-money institutions directly. According to the ECB, they must be able to receive instant euro payments by 9 April 2027. Sending is due on the same date in the euro area and by 9 July 2027 outside it. For banks in the euro area, payee verification has applied since 9 October 2025. Payment service providers offering instant transfers must also screen their clients against EU sanctions lists at least once every calendar day (Art. 5d). If your settlement runs through virtual IBANs, check that your provider's timeline matches yours.
PSD3 and the Payment Services Regulation reached a political deal on 27 November 2025. The deal makes providers cover customer losses when they fail to apply fraud-prevention mechanisms and gives payment institutions non-discriminatory access to bank accounts. The Council's first-reading position is on its agenda for 29 October 2026; there is no confirmed application date yet.
Fintech compliance calendar: dates to watch until 2028#
These are the dates that drive a compliance plan for a payment or crypto firm. Status shows whether the rule already applies.
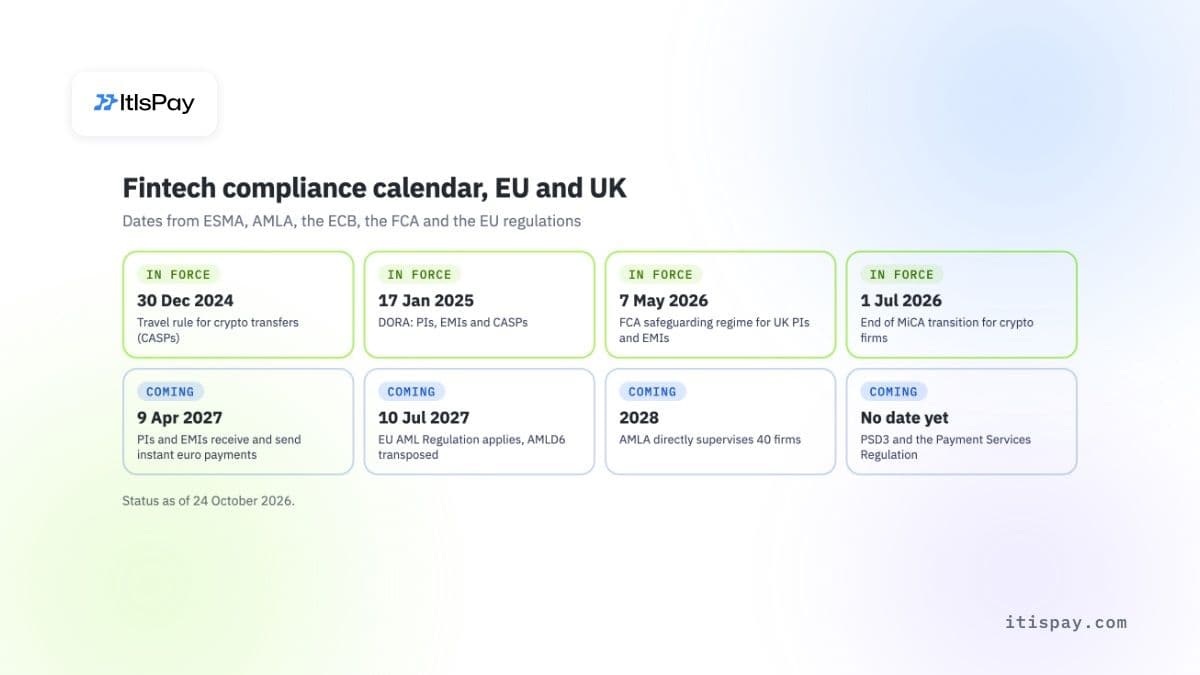
| Date | Rule | Who it hits | Status |
|---|---|---|---|
| 30 Dec 2024 | Travel rule (TFR) for crypto transfers | CASPs | Yes |
| 17 Jan 2025 | DORA | PIs, EMIs, CASPs | Yes |
| 9 Oct 2025 | Payee verification, euro area | Banks in the euro area | Yes |
| 7 May 2026 | FCA safeguarding regime (PS25/12) | UK PIs and EMIs | Yes |
| 1 Jul 2026 | End of MiCA transition | Crypto firms serving EU clients | Yes |
| 9 Apr 2027 | Instant payments: PIs and EMIs receive and send (euro area) | EU PIs and EMIs | Open |
| 9 Jul 2027 | Instant payments: PIs and EMIs send (outside the euro area) | PIs and EMIs in non-euro states | Open |
| 10 Jul 2027 | AMLR applies, AMLD6 transposed | All obliged entities | Open |
| 2028 | AMLA direct supervision of 40 firms | Selected firms | Open |
| No date yet | PSD3 and Payment Services Regulation | PIs, EMIs, banks | Open |
What can a fintech outsource, and what stays with you?#
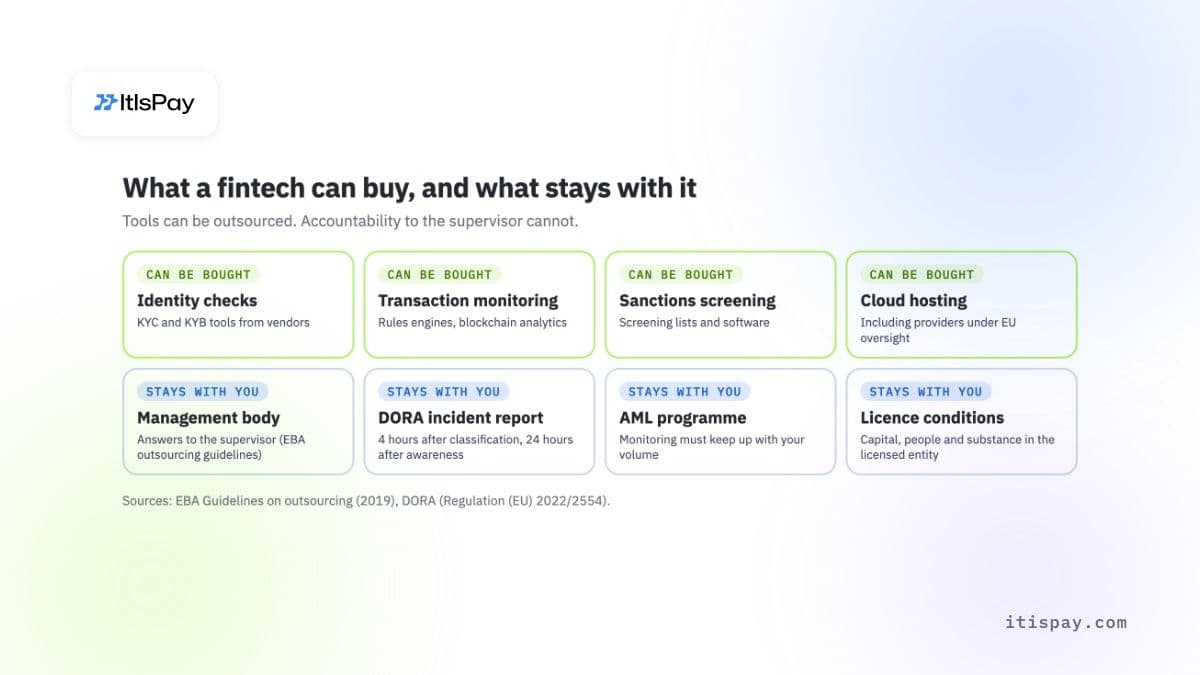
You can buy almost every tool in a fintech compliance framework. Identity checks, transaction monitoring, sanctions screening, blockchain analytics and cloud hosting are all on the market. You cannot outsource the responsibility for them. The EBA's outsourcing guidelines also cover payment and e-money institutions. They state it directly: "The outsourcing of functions cannot result in the delegation of the management body's responsibilities." The same guidelines warn firms not to become "empty shells" or "letter-box entities".
The Monzo case shows what that means in practice. The FCA's final notice records growth from about 250,000 customers in early 2017 to more than 12 million by April 2025. It also states that "rapid customer growth must not come at the detriment of compliance." The controls did not scale with the business.
Where outsourcing does not help
- A vendor's monitoring tool does not answer to the supervisor. Your management body does.
- A critical cloud provider under EU oversight does not file your DORA incident report.
- MiCA protection covers only the authorised EU entity, not group companies or non-EU affiliates.
- A licensed partner covers only the activities it performs under its own licence, not the ones you run yourself.
There is a second route for firms that do not want a licence for every activity. A merchant or platform that wants to accept crypto payments can work through a provider that holds the licence and runs the regulated part. The merchant keeps the customer relationship and the software. The trade-off is control: the partner decides which clients and assets it accepts.
How to build a fintech compliance framework that holds up#
A framework that survives a supervisory review is built in a fixed order, and each step produces a document the supervisor will ask for.
- Map every activity to a licence and a capital requirement, using the table above. Decide what you license yourself and what runs through a licensed partner.
- Name the accountable people: management body, compliance officer, money laundering reporting officer. Supervisors assess them individually.
- Build the AML programme to the AMLR standard now, not in July 2027: risk assessment, customer due diligence, transaction monitoring sized to your volume, travel rule data for crypto.
- Set up the DORA basics: ICT risk framework, register of information, incident classification and a 4-hour reporting runbook.
- Keep the fintech compliance calendar above in front of the board and review it every quarter. Three of its dates fall in 2027.
Preparing a CASP application? Evda helps your team assemble the licence file and check it against MiCA requirements before it reaches the regulator, so gaps surface while they are still cheap to fix. If building your own licence and compliance team is not the right move yet, ItisPay provides the software layer. Our EU-licensed CASP + Payment Institution partner holds the authorisation and carries the regulatory obligations.
This article is for informational purposes only and does not constitute legal or regulatory advice.

